Securing your applications with the CrowdSec WAF
Understand and implement the CrowdSec Web Application Firewall: how it works, how to deploy and configure it, virtual patching, and the OWASP CRS in in-band and out-of-band modes.
- Beginner
- 3 modules
- 15 min
About the course
In this course you'll learn how the CrowdSec WAF works, how to deploy and configure it in real environments, set up virtual patching, and work with the OWASP CRS in both in-band and out-of-band modes. This course is ideal for DevOps engineers, system administrators, and anyone managing web infrastructure who wants a scalable and open source approach to application-layer security.
Course modules
 4:13
Module 1Introduction to the CrowdSec WAF
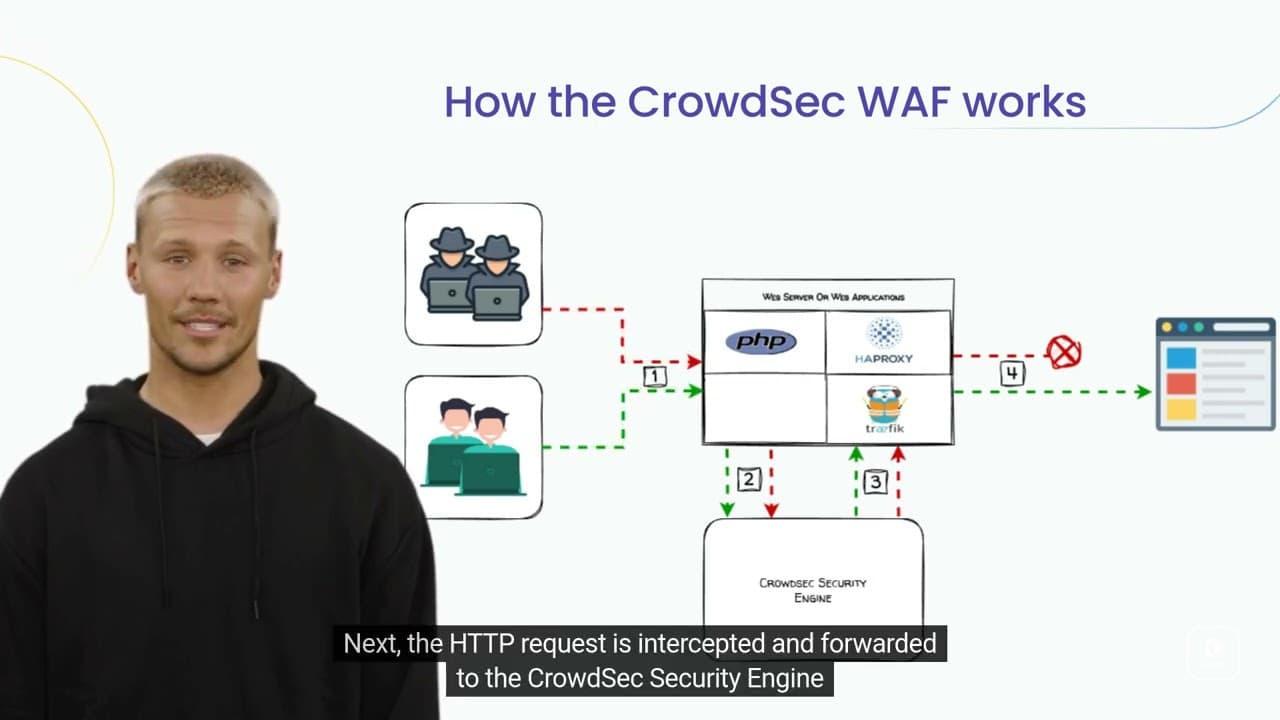
Module 1 provides an introduction to the CrowdSec WAF. We’ll explore what it is, how it fits into the overall CrowdSec architecture, and why it’s a smart choice for application-layer security. We’ll also explain key concepts like inband and out-of-band rule execution.
 5:58
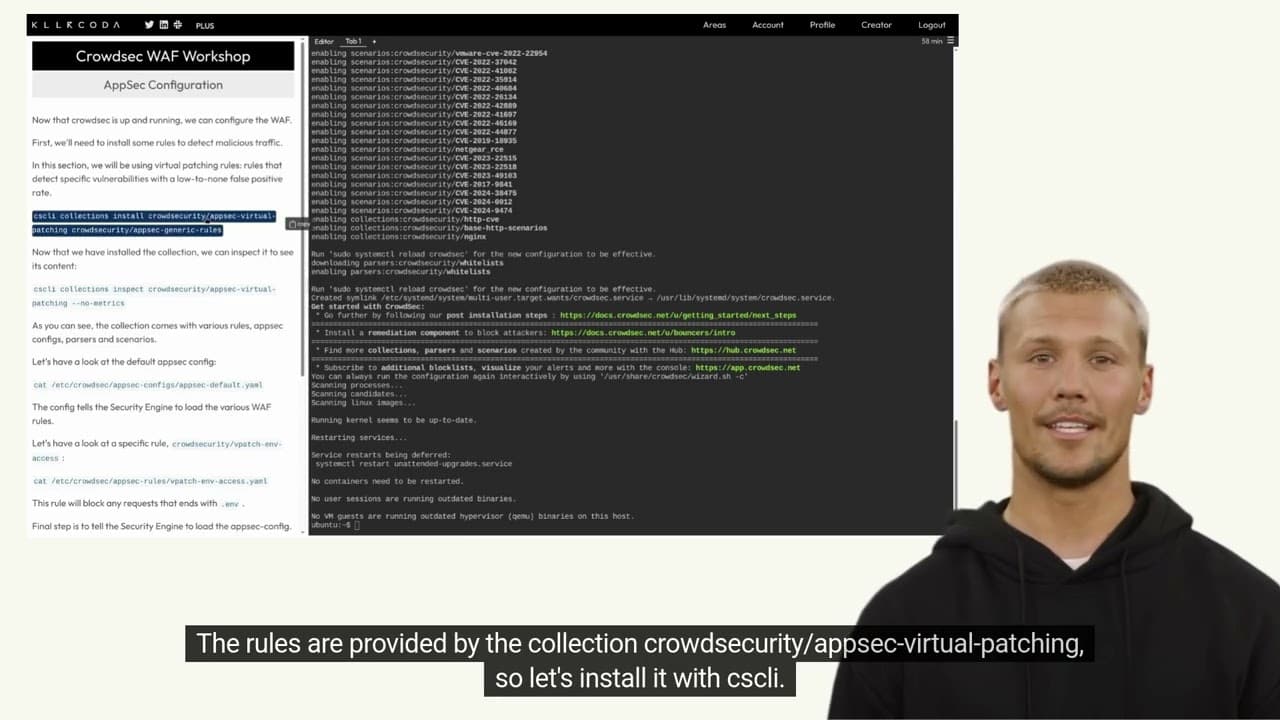
Module 2Installation
Module 1 provides an introduction to the CrowdSec WAF. We’ll explore what it is, how it fits into the overall CrowdSec architecture, and why it’s a smart choice for application-layer security. We’ll also explain key concepts like inband and out-of-band rule execution.
 4:39
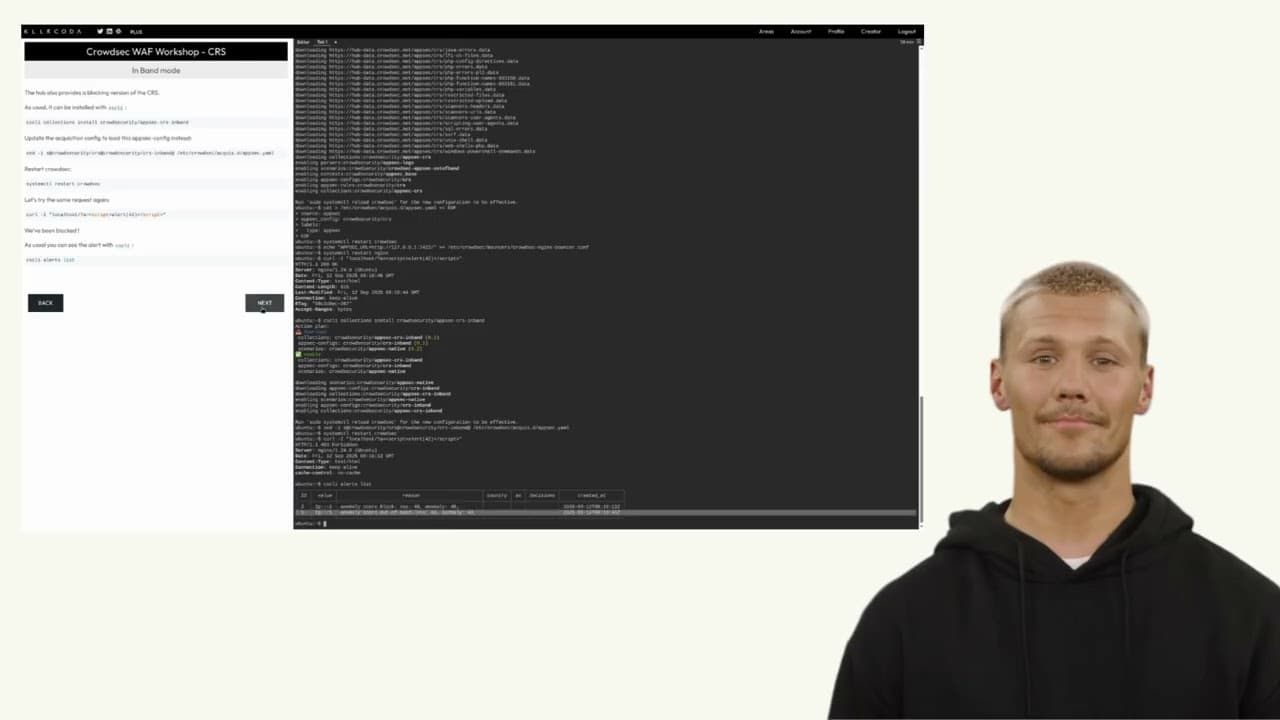
Module 3The OWASP CRS
Module 3 walks through installing the OWASP CRS, using them out-of-band for evaluation, and explaining the advantages and drawbacks of having them in either out-of-band or in-band mode.